Cloud security
Cybersecurity

Emmanuel Odekunle

I design and strengthen AWS environments with least-privilege access, segmented networks, resilient infrastructure, encryption, observability, and practical cost control.

AWS & TerraformSecurity engineeringInfrastructure resilienceEthical HackingDetection Engineering

About

Cloud security and infrastructure engineering with a security-first focus.

I design and propose secure cloud architectures, translate them into production-ready infrastructure using Terraform, and assess environments to identify security and operational risks. My work spans cloud security, infrastructure as code, security assessments, detection and visibility, FinOps and performance testing in order to help teams build secure, scalable, and cost-conscious cloud environments.

Cloud & DevSecOpsGCP, AWS security, IAM and least privilege, CloudTrail, Terraform, CI/CD security and infrastructure hardening.
Defense in depthIndependent controls across identity, network, data, and workloads.
Penetration TestingWeb application and cloud penetration testing, reconnaissance, vulnerability discovery, exploitation, privilege escalation, misconfiguration assessment, and security validation.

Selected work

Security architecture with measurable outcomes

Four projects that combine resilient design, cloud hardening, automation, operational evidence, and controlled validation.

Resilience architecture UsersHTTPS Route 53DNS alias Global AcceleratorAnycast · health-based failover af-south-1 · Primary (active) ALB + WAFpublic subnets · NAT per AZ AZ a · privateECS FargateElastiCache AZ b · privateECS FargateElastiCache RDS Proxy → Aurorawriter + reader · isolated subnets S3 · ECR via VPC endpoints eu-west-1 · Pilot-light DR ALB + WAF2 AZs · pre-provisioned AZ aECS Fargateminimum tasks AZ bECS Fargateminimum tasks RDS Proxy → Aurorasecondary · read-only S3 · ECR replicas Replication: Aurora Global Database · S3 CRR · ECR IAM · multi-Region KMS keys · CloudTrail · Config
Project 01 · ARCHVAULT

Multi-region resilient platform on AWS

Designed a pilot-light disaster recovery pattern for a high-throughput financial workload, balancing availability, recovery targets, peak-load performance, encryption, auditability, and operating cost.

99.95%uptime target
RPO ≤ 5mdata recovery objective
10× loadburst capacity design
Route 53ECS FargateAuroraKMSCloudTrailWAF
Security engineering GOVERNANCE & VISIBILITY IDENTITY & NETWORK WORKLOAD & DATA IAMVPCKMS Least privilege · segmentation · encryption Continuous posture checks · automated response · controlled validation
Project 02 · VaultCloud

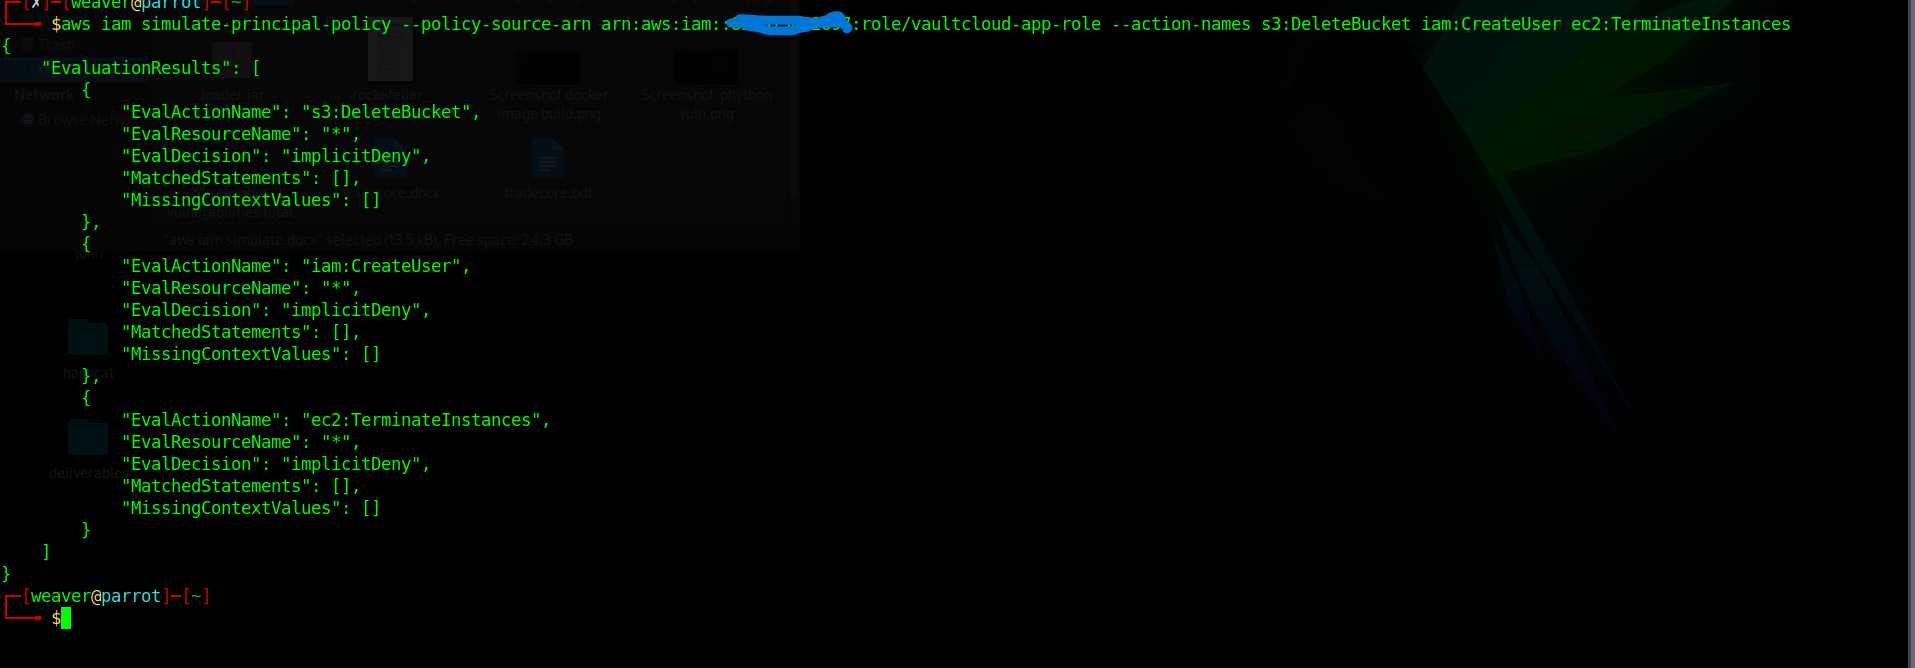
Cloud security hardening and validation

Helped structure a security engineering program across identity, network controls, posture management, workload hardening, automated response, and threat detection. Controls were re-tested through safe, controlled scenarios and supported by clear evidence.

+40%posture score improvement
6 domainssecurity coverage
< 5 minsimulated response time
AWS ConfigGuardDutyEventBridgeLambdaCloudWatchZero Trust
Project 02 · Hardening
TradeCore Africa multi-region AWS architecture diagram
Cloud penetration testing Recon Nmap · Web enum AWS Enum IAM · S3 Policy Access analysis Object Retrieval S3 CREDS Policy disclosure · object retrieval · credential exposure
Project 03 · Pwned Labs

S3 Bucket Policy Enumeration & Unauthorized Access Chain

Conducted an authorized cloud penetration test focused on identifying overly permissive Amazon S3 bucket policies and demonstrating how policy disclosure could be chained into targeted object retrieval and credential exposure.

S3 cloud attack surface
Policy enumeration weakness
Chain access escalation path
AWS S3 AWS IAM Nmap Gobuster John the Ripper
Walkthrough: what I did and what it showed

Scope

An authorized Pwned Labs environment. I was given a target IP address and a set of AWS credentials, and nothing else.

Attack path

  1. Network reconnaissance. An Nmap scan of the target showed the open ports and services. I used the discovered port to reach the web page.
  2. Web enumeration. The page source showed that some of the site's resources were hosted in an Amazon S3 bucket.
  3. AWS enumeration. I configured the provided credentials and tested IAM policy listing, bucket listing, object downloads, object ACL checks and unauthenticated access. Most were denied, because the credentials were narrowly scoped.
  4. Bucket policy enumeration. An unsigned request was denied, so the bucket was not public. The bucket policy itself, however, was readable. It revealed which resources existed and which principals could use them, which let me send a targeted download request for an object I could not list.
  5. Credential extraction. The downloaded file was password protected. John the Ripper recovered the password, and the contents exposed administrative credentials and other privileged information.
  6. Web directory enumeration. Gobuster mapped the directories I could reach with those credentials, which led to confidential data inside the lab.

Small AWS permission weaknesses, chained together, became a serious compromise.

What went wrong

  • Overly permissive bucket policy
  • Policy contents disclosed too much about the bucket
  • Weak access controls around S3 objects
  • Object names relied on as a security boundary
  • Credentials stored in a spreadsheet

How to fix it

  • Apply least privilege to IAM and S3 policies
  • Limit access to bucket policies and metadata to identities that need it
  • Never treat knowing an object name as access control
  • Review bucket policies and ACLs regularly for unintended access
  • Keep credentials in a managed password manager
Cloud infrastructure Users HTTPS AWS Application Layer ALB · HTTPS · Security Groups Security IAM · WAF Application Compute ECS · Fargate · Amplify RDS · Secrets Manager Terraform IaC GitHub OIDC Modular IaC · secure connectivity · secrets · policy enforcement
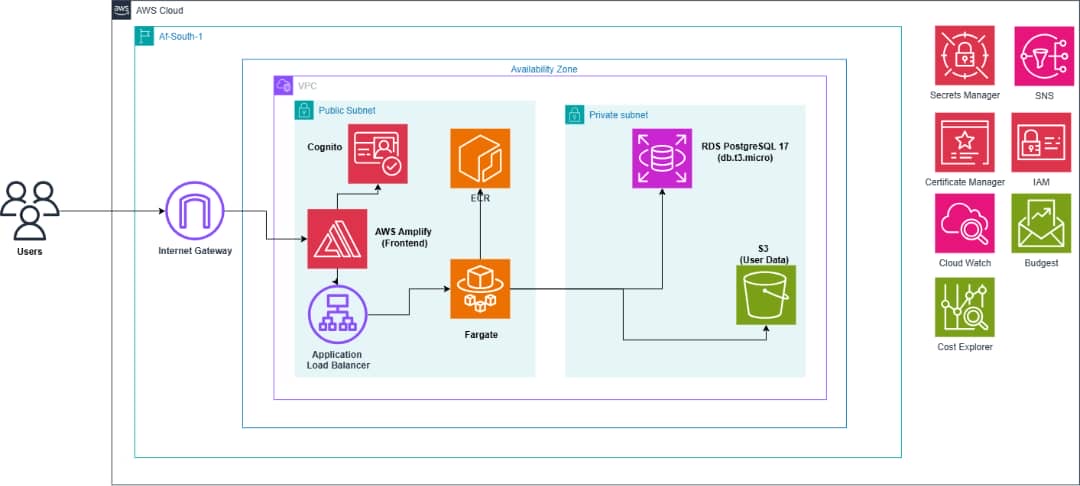
Project 04 · TradeCore FinOps

Secure and Cost Efficient AWS Infrastructure with Terraform

Designed a secure, repeatable AWS environment for a multi-service application using modular infrastructure as code and controlled service connectivity.

Problem: Design a secure, repeatable AWS environment for a multi-service application.

My role: Worked across the Terraform architecture covering networking, ECS, ALB, RDS, Secrets Manager, and Amplify.

Solution: Built a modular infrastructure design with secure service connectivity, HTTPS, secrets management, policy enforcement, and GitHub Actions OIDC.

IaC modular Terraform
HTTPS secure application access
OIDC keyless CI/CD access
Terraform AWS ECS ALB RDS Secrets Manager Amplify GitHub Actions
Project 04 · Architecture
TradeCore Africa Terraform infrastructure architecture diagram

Experience

Hands-on cloud security work

Practical experience across access control, infrastructure as code, network design, penetration testing, API security reviews, monitoring, FinOps, and technical documentation.

Aug 2025 — Present

Cloud Security Intern

Expadox Labs

Designing and securing AWS infrastructure with Terraform, segmented VPC architecture, IAM controls, encrypted services, Secrets Manager, CloudWatch, performance testing, and operational documentation.

Jun 2025 — Present

Cloud Security Intern

PIKA Logistics

Reviewing IAM access rights, API authentication and authorization controls, cloud costs, infrastructure safeguards, and technical documentation.

Capabilities

Development and Security across the cloud lifecycle

01 / CLOUD

AWS security engineering

IAM, VPC, S3, ECS/Fargate, RDS, Secrets Manager, KMS, CloudWatch, CloudTrail, Config, and GuardDuty.

02 / OFFENSIVE

Penetration testing

Web application and cloud penetration testing, reconnaissance, enumeration, vulnerability discovery, exploitation, privilege escalation, and security validation.

03 / INFRASTRUCTURE

Secure architecture

Network segmentation, workload isolation, secure application-to-database communication, encryption, multi-AZ patterns, and disaster recovery planning.

04 / ASSURANCE

Assessment and validation

Cloud security reviews, IAM analysis, API access-control reviews, Linux hardening, packet analysis, and controlled security testing.

05 / OPERATIONS

Performance and visibility

Infrastructure monitoring, audit trails, FinOps, Grafana k6 load testing, evidence collection, and technical reporting.

TerraformLinuxWiresharkNmapBurp SuiteMetasploitGrafana k6TCP/IPDNSHTTP/SDockerJohn the RipperGit

Education & credentials

Education and Training

Education

B.Tech, Science Laboratory Technology

Ladoke Akintola University of Technology · Chemistry (Biochemistry) discipline · Second Class Upper Division

B.Tech
Certification

Introduction to Cybersecurity

Cisco Networking Academy

Certification

Networking Devices and Initial Configuration

Cisco Networking Academy

Training

Ethical Hacking: Beginner to Pro

Linux Professional Institute · Tech Bro Academy